What Are Hashed Emails?: Understanding the Risks, Limitations, and Alternatives

For years, marketers and publishers have relied on third-party cookies for retargeting and monetization, overlooking the myriad problems they posed. Cookies have always raised concerns with lack of consumer consent, device addressability, and poor durability, inviting serious scrutiny and condemnation as a result.
As third-party cookies declined, several identity solutions emerged. One option that has gained traction is the use of hashed emails (HEMs), which transform email addresses into hashed identifiers using cryptographic algorithms. While hashed emails seem well-suited to replace cookies, they also face severe limitations that can impact marketing performance.
In this guide, we will explain what hashed emails are, how they work, their risks and limitations, and why modern marketers are adopting durable, people-based identity solutions like RampID to solve for the cookieless future.
Key Takeaways
- Hashed emails (HEMs) are identifiers created by applying cryptographic hashing algorithms to email addresses.
- Marketers are using hashed emails as an alternative to third-party cookies to support audience planning, activation, and measurement.
- Hashed emails lack persistence, can be reversed, and provide limited visibility across devices and channels, making them a frail identity solution.
- RampIDs offer a stronger alternative to hashed emails through broader matching, support for responsible data use, and stability.
- RampIDs are interoperable with major industry identifiers, supported by 650+ partners, and built to meet global privacy regulation. This unlocks accurate measurement and responsible addressabiltiy at scale.
What is a hashed email?
A hashed email (HEM) is a type of identifier created by applying a cryptographic hashing function (such as SHA-256 or MD5) to a user’s email address. This process converts the email into a unique string of numbers and letters that is not immediately human-readable. Brands, publishers, or platforms can use these hashed strings as identifiers without exposing the raw email address.
For example, the email jane.doe@email.com might be transformed into a long alphanumeric code. If another company applies the same hashing method to the same email address, they’ll get the identical hash, allowing the two parties to recognize a user in common without directly sharing the email itself.
Hashed emailshave gained traction because they offer a marginally more secure alternative to third-party cookies, particularly as marketers look for ways to maintain audience targeting and measurement in a cookieless future. Publishers, advertisers, and identity vendors often promote HEMs as a way to:
- Enable cross-site tracking and activation
- Support audience matching between partners
- Extend the life of authenticated identifiers like emails in a privacy-sensitive format
Why are publishers and advertisers using HEMs?
Publishers and marketers are looking for alternative identity solutions that can help them recognize audiences across channels. Hashed emails allow organizations to use authenticated email addresses as identifiers without sharing the original address.
The push toward hashed emails stems from three major trends:
- Cookie deprecation: As much of the web is already cookie-free, marketers are searching for durable identifiers to maintain addressability.
- Authenticated traffic: With more websites and apps requiring logins, email addresses have become a common anchor for identity.
- Perceived privacy: Because HEMs are not directly human-readable, some marketers view them as a “safe” way to share and activate customer data.
However, HEMs carry major drawbacks that make them less effective and secure than durable, tokenized identifiers such as LiveRamp’s RampID
What are the limitations of hashed emails?
While hashed emails are often positioned as a quick fix for a cookieless future, they carry serious limitations that undermine their effectiveness. From security concerns to weak persistence and measurement challenges, HEMs fail to provide the durability, privacy, and accuracy that modern marketers need.
The key limitations include:
- HEMs aren’t secure
- An email address is not a comprehensive online identity
- An email address is not persistent
- HEMs weaken measurement
Hashed emails aren’t secure
Proponents of hashed emails hail the solution’s cryptographic, one-way encryption process that creates a code unique to the email. However, HEMs are a universal identifier—the same HEM is sent by brands to all activation endpoints. While an email in hashed form may not be human readable, they are standardized algorithms, and many firms are now offering services that can reverse email hashing to correctly guess consumers’ email addresses, identifying users on a personally identifiable level. Of equal or greater concern is that these email lists can be, and are, easily repurposed and rehashed to violate user privacy.
An email address is not a comprehensive online identity
Identity resolution providers such as LiveRamp provide value by tying multiple identifiers (including email) to a real, person-based identifier. Using email address data that a user declares as the base of identity will create a brittle conception of the consumer that may not extend comprehensively across devices, households, and environments that require a log-in using a different identifier. Since HEMs don’t protect directly identifiable personal data, they're an inappropriate solution for data collaboration with other parties, and because they’re not a durable people-based identifier, matching identity for the purposes of data activation is weak.
An email address is not persistent
Email addresses change with each new job, with new software, and with maturity. Email addresses are elective identifiers, and consumers can elect to change them at any point, often without any fee. Inconsistencies also create fragile matching. HEMs require both parties to not only have the same individual email address, but that address must be stored in the same syntax for HEMs to join. HEMs also can’t match against other common directly identifiable personal data, such as NAP data (name and postal information), or against digital device identifiers used to recognize visitors and prospects. This match weakness is exacerbated in programmatic bidstreams, where each call from brand to DSP to SSP to publisher will go through this same probabilistic match test and cause drop-off in audience reach.
HEMs weaken measurement
Accurate audience measurement depends on durable omnichannel person-based identifiers that are stable even when the consumer updates their directly identifiable personal data. As noted above, HEMs change when a customer’s email changes, and HEMs don’t resolve to single individuals across channels, harming long-term incrementality measurement for attribution or building training data for machine learning.
Hashed emails vs. RampID: What's the difference?
Hashed emails and RampID are both designed to help marketers navigate a cookieless future, but they solve different challenges. While HEMs offer a step forward from cookies, RampID provides a more durable, secure identifier that works across the ecosystem.
The table below highlights the key differences:
How RampID solves the challenges presented by hashed emails
While HEMs may appear to offer a quick fix for identity, they fall short in durability, privacy, and accuracy. RampID was designed to overcome these weaknesses, giving marketers and publishers a secure, people-based solution that scales across the ecosystem and provides the following benefits:
- Stronger and broader matching
- Responsible use of data
- Persistence over time
- Ecosystem-wide interoperability
- Future-ready identity
Stronger and broader matching
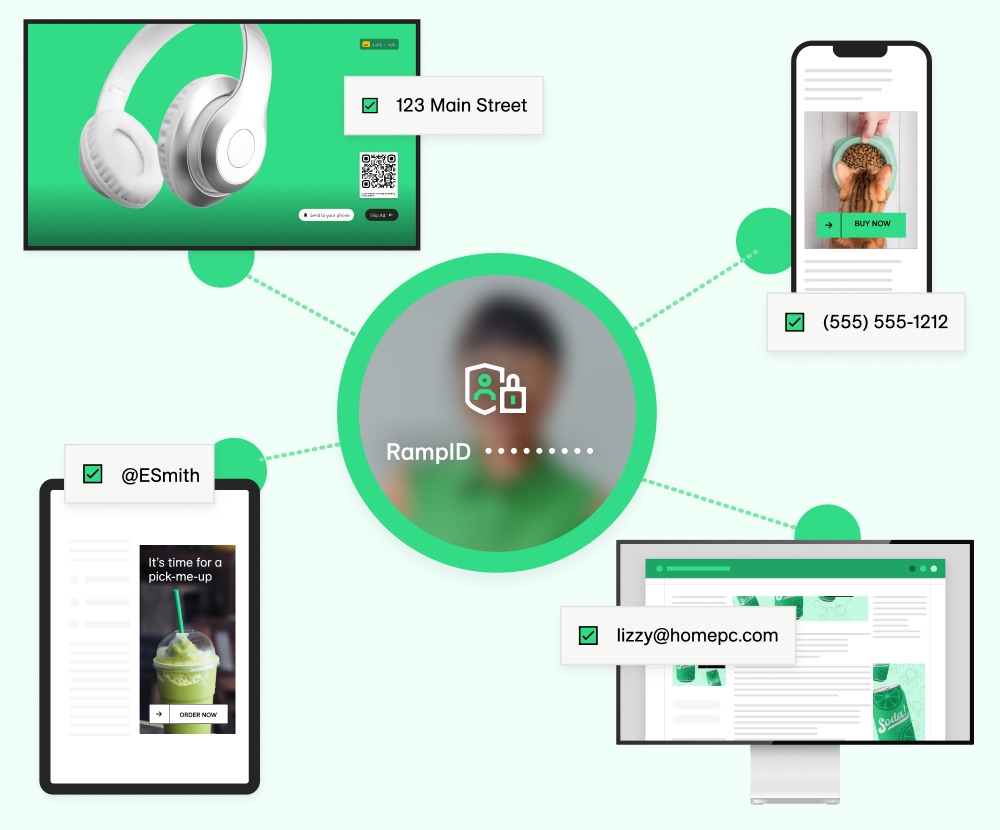
Unlike HEMs, which require both parties to have the exact same email address formatted and hashed in the same way, RampIDs can match across multiple identifiers. They work whether data is based on email, postal, phone, cookies, MAIDs, or IPs, reducing audience drop-off and extending addressability across environments. RampID matching has been proven to deliver 44% higher match rates than HEM-to-HEM matching across leading publishers. In a recent Comscore study, LiveRamp's identity graph - the backbone of RampID - achieved a match rate of 99.5%.
Responsible use of data
HEMs are reversible, exposing consumers to tracking and data leakage risks. RampIDs are tokenized and obscure directly identifiable personal data, assigning unique encodings for each partner. That means two companies referencing the same individual will see different RampID formats, eliminating universal tracking threats and protecting consumer trust.
Persistence over time
Email addresses change often, but RampIDs remain stable even as names, addresses, or digital devices shift. LiveRamp maintains these links in its longitudinal identity graph, ensuring consistent recognition of individuals and households over time. This persistence enables accurate attribution, incrementality measurement, and machine-learning training.
Ecosystem-wide interoperability
No identifier has more operational support through the programmatic ecosystem than RampID. It is accepted across DSPs, SSPs, publishers, and more than 650 global partners, enabling marketers to activate, measure, and optimize campaigns without loss of scale.
Future-ready identity
RampIDs are interoperable with other industry identifiers like UID2, OpenID, and Lotame Panorama ID, giving marketers flexibility in their tech stack. RampID has been developed to support customers' privacy program requirements and provide tools to enable compliance as privacy regulations evolve.
How LiveRamp can help you move beyond hashed emails
Hashed emails can support some identity use cases, and may look like an easy replacement for cookies, but their weaknesses in security, persistence, and accuracy make them a fragile solution. RampIDs provide the durability, privacy, and scale needed for modern marketing.
Publishers and marketers should have their choice of IDs to activate first-party data, which sometimes means using multiple identities. LiveRamp’s neutral infrastructure is accessible to any identity that meets consumer privacy needs. As more interoperable IDs are added, customers will continue to have flexibility and security in their tech stacks as they strive to create meaningful connections with their consumers.
Ready to move beyond HEMs? Contact LiveRamp to learn how our identity resolution solutions can help you develop a future-ready data strategy and unlock addressability at scale.
Hashed Email FAQs
What does a hashed email look like?
A hashed email is a long string of letters and numbers created by applying a hashing algorithm (like SHA-256) to an email address. For example, jane.doe@email.com might become something like 7c4a8d09ca3762af61e59520943dc26494f8941b.
How do hashed emails work?
Hashed emails are created by normalizing plain-text email addresses by removing extra spaces and converting uppercase letters to lowercase. A hashing algorithm then converts each normalized address into a standardized, fixed-length alphanumeric string. This allows companies using the same data to match records without exchanging the email addresses.
What are common uses for hashed emails in marketing?
Marketers use hashed emails for audience matching and onboarding, targeted advertising, cross-device engagement, conversion tracking, attribution, suppression, and campaign measurement. They can also support identity resolution by matching authenticated customers across advertising platforms and publishers without exchanging email addresses.
How do hashed emails (HEMs) enable identity resolution for marketers?
Hashed emails help marketers match customer records across datasets without sharing plain-text email addresses, reducing the risk of personal information exposure. However, hashing only pseudonymizes the address; it does not make it anonymous. An HEM can still be linked to a person by hashing known or guessed addresses and comparing the values.
Can hashed emails support cookieless advertising?
Hashed emails can help marketers recognize authenticated users in environments where third-party cookies are unavailable. However, because they rely on a single email address, HEMs hold limitations in persistence, interoperability, and measurement. Many organizations substitute hashed emails for more durable, people-based identity solutions.
What is the difference between a hashed and an unhashed email address?
An unhashed email is the plain-text address you use every day (e.g., jane.doe@email.com). A hashed email is the same address run through an algorithm that produces an obfuscated alphanumeric string. The unhashed version is directly identifiable, while the hashed version is meant to mask it – though it can often still be traced back to the original email.
Are hashed email addresses considered personally identifiable information (PII)?
Yes. Even though hashed emails aren’t immediately human-readable, they are still considered personally identifiable information (PII). That’s because the hash can often be reversed or matched back to an individual, making it possible to re-identify the person behind the email.
How do RampIDs compare to hashed emails?
RampIDs drive better experiences by enabling accurate omnichannel campaigns, helping companies protect privacy through non-reversible IDs, and delivering more reliable analytics. They’re stable over time, interoperable with other IDs, supported by 500+ partners, and enable compliance – giving marketers both flexibility and consumer trust that HEMs can’t match.
Identity Explainer
How to fuel unified customer experiences with connected data
Learn 5 ways to create better customer experiences with data collaboration.
Learn more about the power of data collaboration. Download the eBook, 5 Ways to Create Better Customer Experiences Using Data Collaboration